
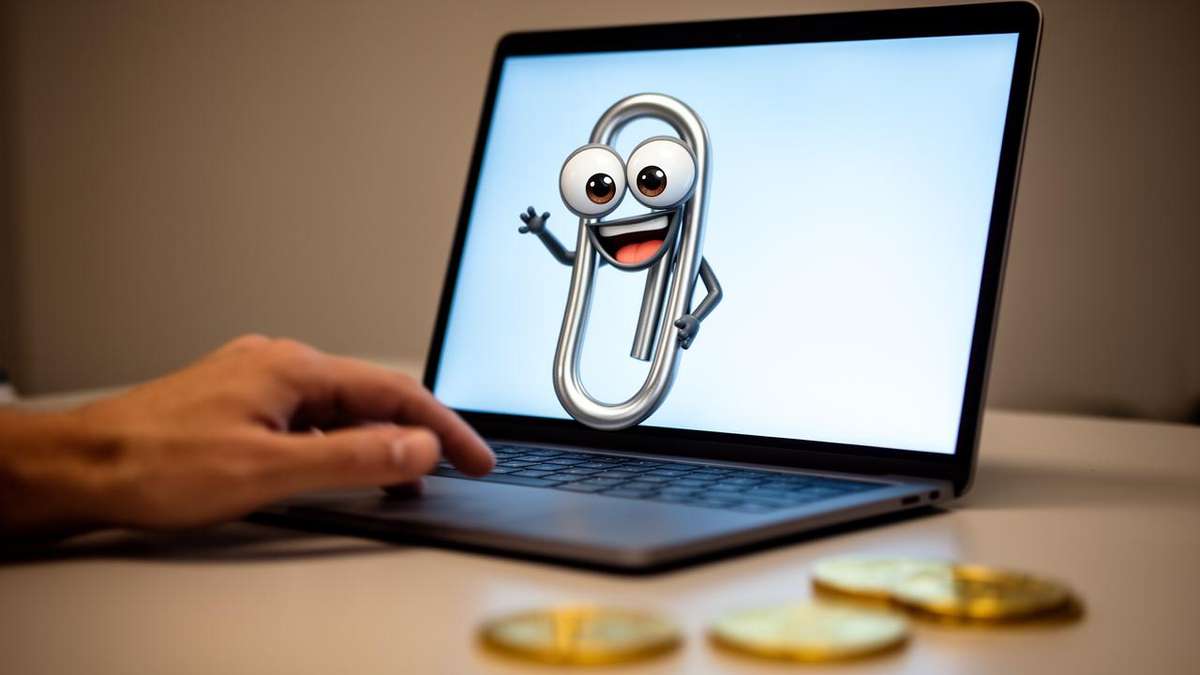
Hackers seized control of Microsoft's official X account on October 1, briefly turning one of the platform's most-followed corporate profiles into a promotional vehicle for a fraudulent cryptocurrency themed around Clippy, the retired animated paperclip assistant. The company confirmed the breach in a statement to The Verge, saying the account has since been secured and the unauthorized posts removed.
Microsoft's X Account Briefly Hijacked to Promote Fake Clippy Crypto Token
Hackers seized control of Microsoft's official X account on October 1, briefly turning one of the platform's most-followed corporate profiles into a promotional vehicle for a fraudulent cryptocurrency themed around Clippy, the retired…
finance.biggo.com
Publisher
Oct 4, 2026 at 6:07 PM UTC · 3 Min. Lesezeit
Key Signal
13M+ Microsoft X followers
Last Updated
vor 15 Stunden
Übersetzung…
The @Microsoft account, which counts more than 13 million followers, began following a crypto account called @clippymsftcto, reposted one of its messages, and had its profile picture swapped to Clippy during the takeover. The attackers used the nostalgic character to push a token dubbed $Clippy, promising that Microsoft would bring the assistant back if a post reached 500,000 likes.
Promotional material also claimed the token was paired with Microsoft stock, using the label "MSTF" to suggest a corporate connection. No legitimate relationship supported that claim, and X suspended the fraudulent account. Details about how attackers accessed the account and how much money the campaign generated remain unclear.
A fabricated apology
Shortly after the promotional posts appeared, a message surfaced on the compromised account that appeared to be a Microsoft apology rejecting the scam and threatening legal action against those responsible. But according to BleepingComputer, the company never published that statement either. The fabricated response appeared designed to confuse followers about whether Microsoft had regained control of the account, blurring the line between attacker activity and authentic corporate communication.
Article Intelligence
Topics
Sponsored
Ad
NewsLayerLearn more
NewsLayer Premium
Unlock deeper intelligence.
Ad-free reading, exclusive research, and real-time onchain insights.
Go Premium