
Post-quantum migration can become unmanageable when enterprises treat every cryptographic dependency as a single replacement project. As organizations move from quantum awareness to implementation, the transition reaches across applications, infrastructure and suppliers, making coordination as important as algorithm selection.
LGT advances post-quantum migration with banking pilot
Post-quantum migration can become unmanageable when enterprises treat every cryptographic dependency as a single replacement project. As organizations move from quantum awareness to implementation, the transition reaches across…
SiliconANGLE
Publisher
Sep 17, 2026 at 5:51 PM UTC · 4 min de lecture
Traduction…
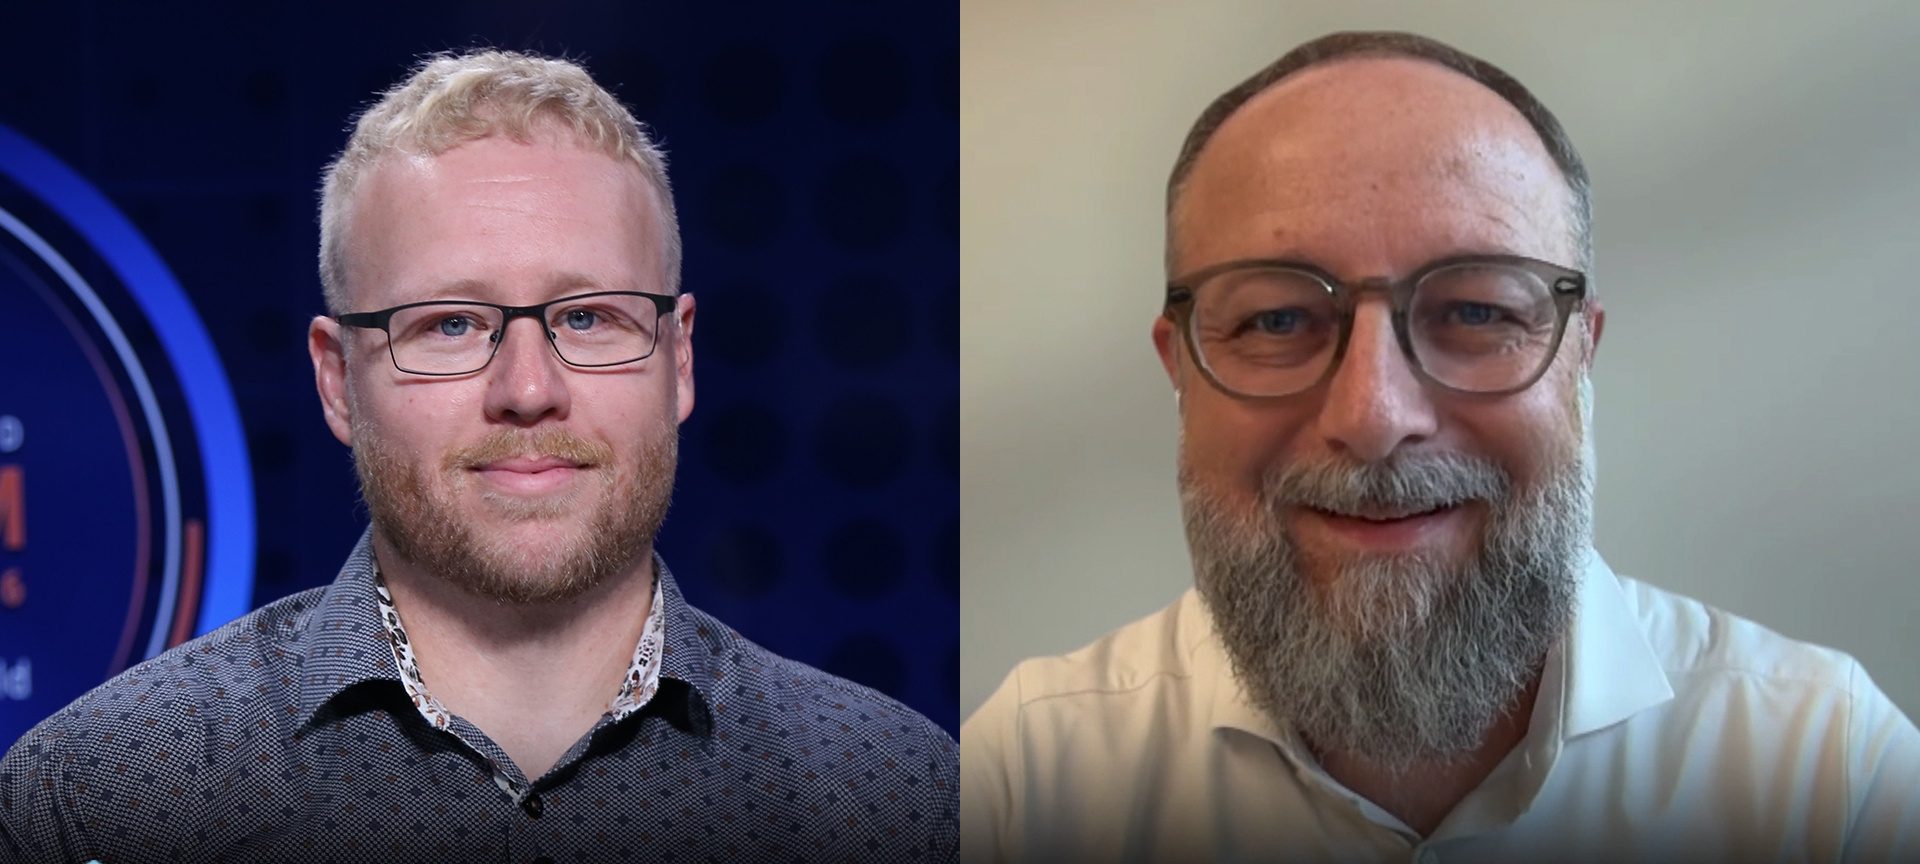
At LGT Financial Services AG, quantum safety entered formal risk discussions in 2022, when the topic was raised at the firm’s annual risk and cyber risk management meeting. The company later created a competence center to connect security operations, architecture, public key infrastructure, application owners, vendors and risk stakeholders, according to Christian Pfister (pictured, right), team leader, IT security operations, and lead for LGT’s Quantum Safe Competence Center.
“Quantum safety is a resilience and risk management issue,” he said. “The key question for leadership was straightforward: Which information must remain confidential long enough that it may be exposed to a future cryptographic break? We then explained that waiting until there is a cryptographically relevant quantum computer would leave too little time to identify dependencies, upgrade product, coordinate suppliers and safely migrate.”
Article Intelligence
Topics
Related Coverage
 PolicyJPMorgan Says SEC, CFTC-Led Crypto Regulation Lacks Staying Power After Clarity Act Senate Setbackil y a 11 minutes · 1 min read
 CryptoSEC Green Lights Tokenized Stock Trading Despite Clarity Act Failil y a une heure · 1 min read
 QuantumNew benchmark puts quantum computers to the test and reveals their limitationsil y a une heure · 1 min read
Sponsored
Ad
NewsLayerLearn more
NewsLayer Premium
Unlock deeper intelligence.
Ad-free reading, exclusive research, and real-time onchain insights.
Go Premium