
An attacker exploited a custom module connected to an Ethereum Safe wallet in an attempt to extract roughly $7.7 million in rsETH, only to have the funds intercepted by an MEV bot.
breaking
ETH wallet exploit backfires as MEV bot captures $7.7M, Kelp freezes address
An MEV bot known as “Yoink” front-ran an attacker attempting to exploit a custom Safe module, capturing the stolen rsETH before Kelp temporarily froze the receiving address.
Cointelegraph by Nate Kostar
Publisher Cointelegraph
Sep 15, 2026 at 3:21 PM UTC · 1 分で読める

Entities
ethereum
Last Updated
7時間前
翻訳中…
According to blockchain security firm Blockaid, the attacker used a public keeper multicall to direct a custom Uniswap v4 liquidity module into an attacker-created hooked pool, where aEthrsETH was unwrapped into rsETH.
Blockaid identified the affected wallet as a Safe belonging to an unidentified user and said about $7.73 million in rsETH had been lost at the time of its initial report.
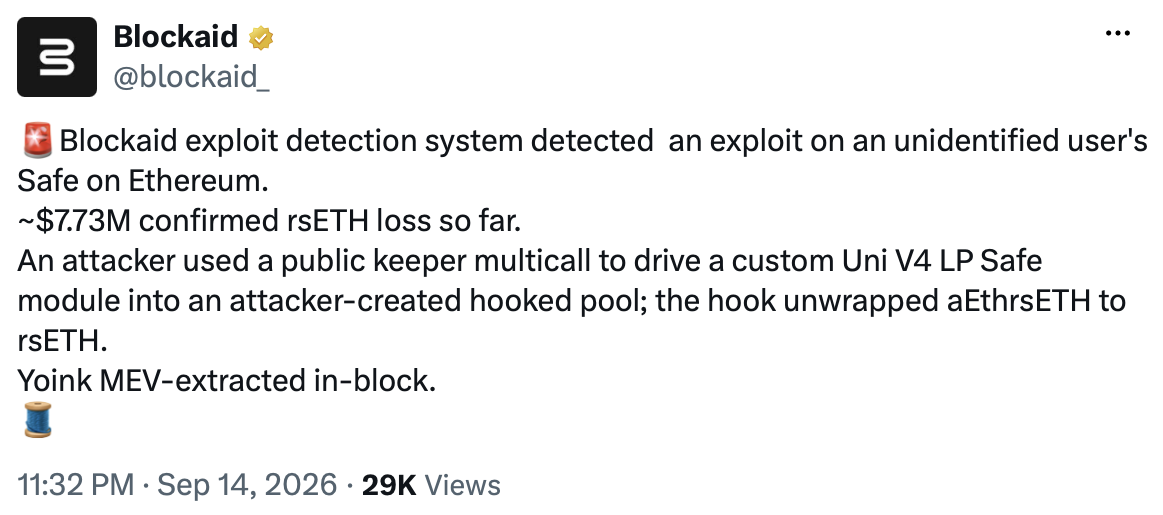
Source: Blockaid
The attack was then front-run by an MEV bot known as Yoink, an automated program that monitors blockchain transactions for profitable opportunities. The bot captured the rsETH before the original exploiter could take control of the funds, while Etherscan data shows Yoink transferred about 18.93 ETH, worth roughly $46,000, to an address labeled as a block builder in the same transaction.
Kelp, the protocol behind rsETH, subsequently placed the address that received the funds under a 24-hour pause, temporarily preventing the tokens from being transferred. “This is a precautionary, wallet-level measure only,” Kelp said. “Kelp contracts are safe, rsETH remains fully backed.”
Market Context
Ethereum
ETH
$2,410
-4.19% (24H)
Market Cap
$292.4B
Circulating Supply
122.1M ETH
24H Volume
$19.4B
24H High
$2,526
Article Intelligence
Topics
Related Coverage
 Artificial IntelligenceAI Crypto Crime: Deepfakes, Fake Support, Phishing2時間前 · 4 min read
 CryptoElizabeth Warren Says Crypto Regulation Must Advance, but She Can’t Back Current CLARITY Act1時間前 · 1 min read
 CryptoBIS paper finds major gap in Bitcoin onchain transfer estimates2時間前 · 2 min read
Sponsored
Ad
NewsLayerLearn more
NewsLayer Premium
Unlock deeper intelligence.
Ad-free reading, exclusive research, and real-time onchain insights.
Go Premium