
AI agents that have not run recently retain credentials and connections to company systems, according to Arrakis Security’s 2026 Autonomous Agents Threat Report. About 76% of enabled agents examined had not run in 60 days, leaving access available through inactive software.
Forgotten AI agents may still access sensitive company data
AI agents that have not run recently retain credentials and connections to company systems, according to Arrakis Security’s 2026 Autonomous Agents Threat Report. About 76% of enabled agents examined had not run in 60 days, leaving…
Help Net Security
Publisher
Oct 26, 2026 at 5:30 AM UTC · 3 min de leitura
Traduzindo…
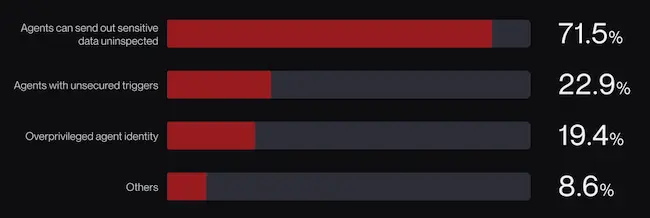
Agents by exposure family (Source: Arrakis Security)
The analysis covered thousands of agents in customer production environments over a 12-week period. These programs can read and write data, call tools and start workflows, giving them the ability to perform tasks across business services.
“When an agent stops being used, nobody removes anything, because in most companies nobody owns it,” said Tal Baron, CEO of Arrakis Security.
Dormant agents retain working access
Inactivity was measured from each agent’s last recorded run. Forty-four percent had not run in 180 days. Some agents operate on weekly, monthly or quarterly schedules, making the inactivity period relevant to their classification.
About a quarter of dormant agents could still be started through an unsigned webhook from outside the organization.
Unsecured triggers accept requests an agent cannot verify. In some cases, anyone who knows the URL can make the agent run. Other exposures included accepting requests from addresses that should be rejected or accepting the same request after it had already been used.
Article Intelligence
Sponsored
Ad
NewsLayerLearn more
NewsLayer Premium
Unlock deeper intelligence.
Ad-free reading, exclusive research, and real-time onchain insights.
Go Premium