
Attackers built a website for a fake AI crypto trading agent and used it to install Needle Stealer, malware that replaces a victim’s browser wallet with a copy that sends the wallet password to the attacker. HP caught the campaign between April and June 2026.
Fake AI trading agent steals crypto wallet passwords
Attackers built a website for a fake AI crypto trading agent and used it to install Needle Stealer, malware that replaces a victim’s browser wallet with a copy that sends the wallet password to the attacker. HP caught the campaign…
Help Net Security
Publisher
Sep 17, 2026 at 8:00 AM UTC · Updated 2 ngày trước · 3 phút đọc
Đang dịch…
The Needle campaign targets people who download AI agents from search results or ads, and users of seven browser wallet extensions, among them MetaMask, Coinbase Wallet and Phantom. HP also caught QR code phishing that moves victims onto their phones.
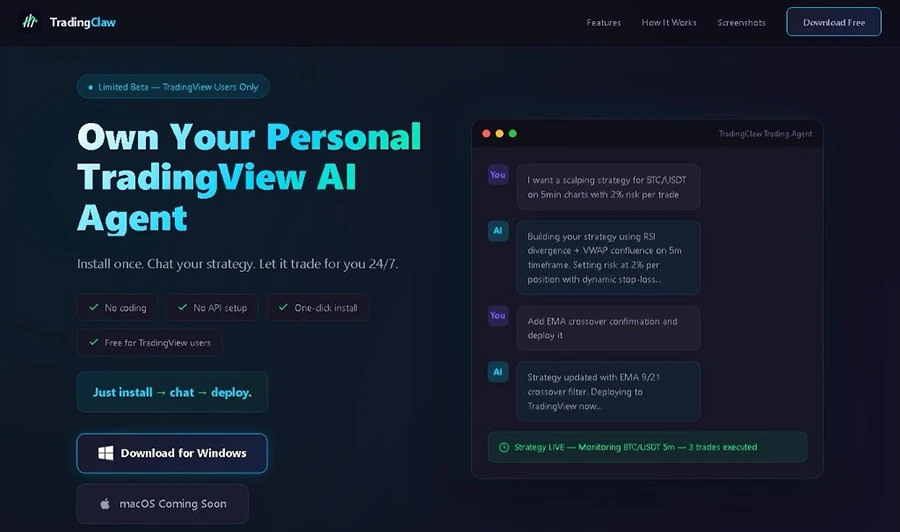
Example of a website promising an installer for an AI trading agent (Source: HP)
The installer is genuine Microsoft software
The site, tradingclaw[.]pro, gave its bot a name that echoes a well-known AI assistant and promised an agent that trades crypto around the clock. Inside the ZIP download, Trading Agent.exe is OLEView, a Microsoft-signed program, so Windows SmartScreen’s reputation check trusts it. Its only purpose is to get past that check. When it runs, it loads iviewers.dll, the malicious file beside it, a trick called DLL side-loading.
That DLL runs Needle Stealer inside a freshly started legitimate process, a technique called process hollowing. Needle looks for any of the seven wallet extensions, kills the browser, and unpacks a malicious copy into the extension’s folder. The fake extension then contacts the attacker’s command server and hands over whatever password the victim types. With the wallet ID and password, the attacker controls the funds.
Article Intelligence
Sponsored
Ad
NewsLayerLearn more
NewsLayer Premium
Unlock deeper intelligence.
Ad-free reading, exclusive research, and real-time onchain insights.
Go Premium