
Hardware wallet producer Trezor announced it would reduce its number of resellers as a “preventive step, taken out of an abundance of caution,” following reports that malicious implants had been installed in devices made by competitor Ledger.
Trezor reduces resellers as a ‘preventative step’ amid Ledger tampering reports
CCO Danny Sanders said he had notified certain hardware wallet resellers that they would be removed from Trezor’s list of authorized entities starting Jan. 1.
Cointelegraph by Turner Wright
Publisher Cointelegraph
Oct 13, 2026 at 7:07 PM UTC · 2 phút đọc
In a Tuesday X post, Trezor said there was “not a single piece of evidence that [its] devices have been compromised” after reports that Ledger hardware wallet users had found malicious implants that exposed recovery phrases.
However, Trezor said that it would reduce the number of its resellers, citing “recent supply-chain incidents.” Chief commercial officer Danny Sanders added that he had notified certain resellers that they would be removed from the company’s list of authorized entities on Jan. 1, and would halt shipments of Trezor devices starting on Tuesday.
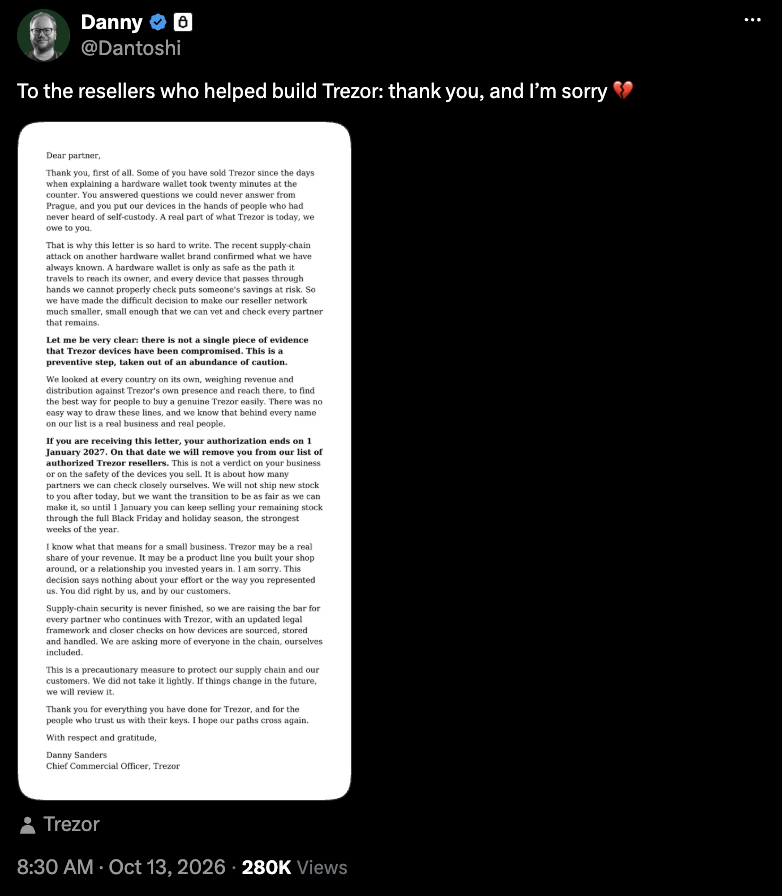
Source: Trezor CCO Danny Sanders
Trezor’s response came just days after Ledger confirmed that at least one of its devices purchased by a Southeast Asian reseller contained an unauthorized hardware implant, potentially leading to millions of dollars in losses for users. The wallets, sold by reseller CryptoBilis, captured recovery phrases and transmitted them over cellular networks.
“Our setup checks are built to catch counterfeit devices and modified firmware,” a Trezor spokesperson told Cointelegraph. “The implant found in a device bought from CryptoBilis works differently. This is a unique way of tampering with the device, which doesn’t modify the firmware, but reads information on the screen and later sends it to the attacker. So far, we have not seen this specific type of attack on Trezor devices in the real world.”
Article Intelligence
Sponsored
Ad
NewsLayerLearn more
NewsLayer Premium
Unlock deeper intelligence.
Ad-free reading, exclusive research, and real-time onchain insights.
Go Premium