
breaking
XRP Ledger’s Payment Engine Had a Counterfeiting Bug Hiding Since 2015
An integer overflow in the payment engine, dormant since 2015, could have let an attacker mint spendable XRP beyond the token’s total supply.
Decrypt Agent
Publisher Decrypt
Oct 12, 2026 at 3:56 PM UTC · 2 phút đọc
Key Signal
2015 Bug present since
Entities
xrp
Last Updated
2 ngày trước
Đang dịch…
- XRP Ledger maintainers disclosed and patched a critical payment-engine overflow bug, reported via bug bounty in September, that could have let an attacker create counterfeit XRP.
- The flaw sat unnoticed since 2015 because no normal payment triggers it, and the ledger’s “no XRP created” safety check used the same broken arithmetic.
- There is no evidence the bug was ever exploited, XRP Ledger devs say.
Developers behind the XRP Ledger have disclosed and fixed a critical vulnerability that, left unaddressed, could have let an attacker conjure XRP out of thin air, a flaw that sat dormant in the network’s code for roughly a decade.
In a disclosure published Friday, the ledger’s maintainers said a researcher reported the bug through the XRPL bug bounty program in September. The issue was an integer overflow in the payment engine, the part of the software that processes payments.
When a single payment consumed hundreds of specially crafted offers from the order book, the sum of what the buyer owed exceeded the maximum value the system could store and “wrapped around” to a tiny number. The engine paid each seller in full but charged the buyer almost nothing, with the difference amounting to newly minted XRP that should never have existed.
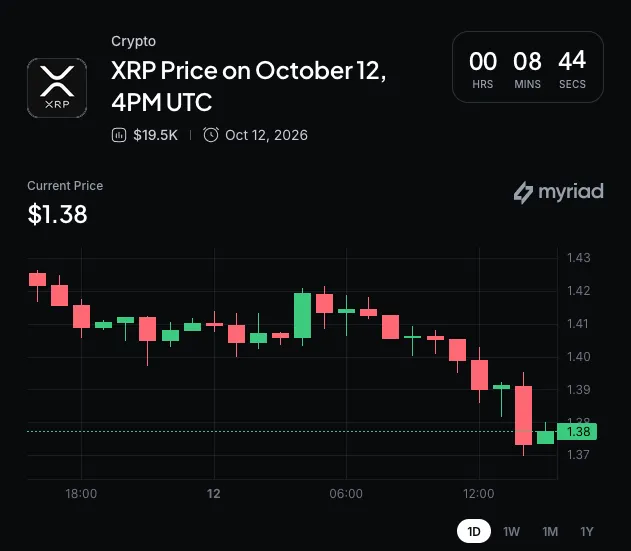
Market Context
XRP
XRP
$1.33
-2.97% (24H)
Market Cap
$83.8B
Circulating Supply
63.1B XRP
24H Volume
$1.9B
24H High
$1.39
Article Intelligence
Key Entities
Topics
Related Coverage
 CryptoLedger Suspends Southeast Asian Resellers During $90 Million Crypto Wallet Hack Investigationmột giờ trước · 2 min read
 CryptoJonathan Spalletta Crypto Hack Conviction in $53M Case: What Did the Jury Find?một giờ trước · 3 min read
Sponsored
Ad
NewsLayerLearn more
NewsLayer Premium
Unlock deeper intelligence.
Ad-free reading, exclusive research, and real-time onchain insights.
Go Premium