
The Jewelbug hacker group has been carrying out espionage operations targeting governments and militaries while also engaging in cryptocurrency fraud.
breaking
Hackers breach govt webmail while running parallel crypto fraud
The Jewelbug hacker group has been carrying out espionage operations targeting governments and militaries while also engaging in cryptocurrency fraud.
BleepingComputer
Publisher
Aug 13, 2026 at 6:15 PM UTC · 4 分钟阅读
Key Signal
15 government webmail tenants compromised
Last Updated
2 个月前
翻译中…
Although the threat actor has targeted government agencies and organizations in critical sectors, including defense, telecommunications, education, and aviation, its cryptocurrency-related activity suggests that they may also operate as a hack-for-hire group that seeks to profit from cybercrime.
In a recent operation, Jewelbug (also known as Earth Alux and REF7707) compromised webmail accounts belonging to 15 government tenants as part of a campaign targeting a country in the Middle East.
Researchers at Symantec found that the espionage campaign and the cryptocurrency fraud were conducted from the same control panel.
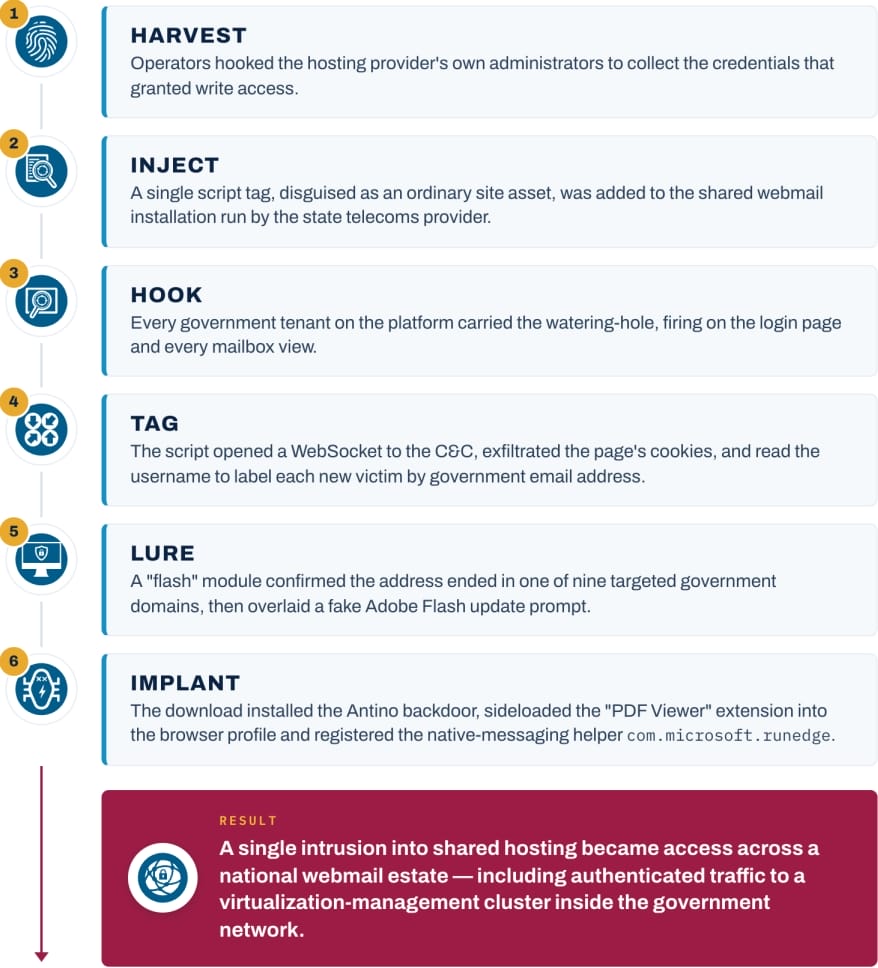
The China-based hacker group gained write access to the shared webmail installation and inserted a malicious script into its common template. The script then ran on login pages and mailbox views across 15 tenants.
Source: Symantec
After execution, the script established a WebSocket connection to the attacker's command-and-control (C2) server, exfiltrated webmail cookies, and retrieved the user's email address to determine whether it belonged to a targeted government domain.
Article Intelligence
Topics
Related Coverage
 CryptoCrime podcaster targeted in Facebook hacking and bitcoin scam4 小时前 · 1 min read
 CryptoQubic Pushes Back on Hack Claims: Weak Wallet Seeds Were to Blame5 小时前 · 1 min read
Sponsored
Ad
NewsLayerLearn more
NewsLayer Premium
Unlock deeper intelligence.
Ad-free reading, exclusive research, and real-time onchain insights.
Go Premium