
Update, November 17, 17:12 UTC: Optimizely has confirmed the incident. Its status page says an unauthorized party exploited a vulnerability in Experimentation and added malicious JavaScript to some customer projects, and a spokesperson told Gizmodo the flaw was in the account signup flow. Optimizely says it has fixed the flaw and removed the injected code. Scott Helme has also published the full list of affected organizations. We have revised this post to match, and corrected earlier statements about the loader, the exposure window and the wallets. Later on November 17 we added Optimizely's fuller statement, the first responses from affected companies, a lower estimate of what victims lost, and more attacker infrastructure. We also corrected the TRON row of the wallet table, which wrongly described outgoing transfers as incoming.
OPTIMJACK: Optimizely-Hosted Scripts Loaded a Crypto Clipper and Card Skimmer on 178 Organizations
Update, November 17, 17:12 UTC: Optimizely has confirmed the incident. Its status page says an unauthorized party exploited a vulnerability in Experimentation and added malicious JavaScript to some customer projects, and a spokesperson…
StepSecurity
Publisher
Nov 18, 2026 at 2:51 AM UTC · 17 分钟阅读
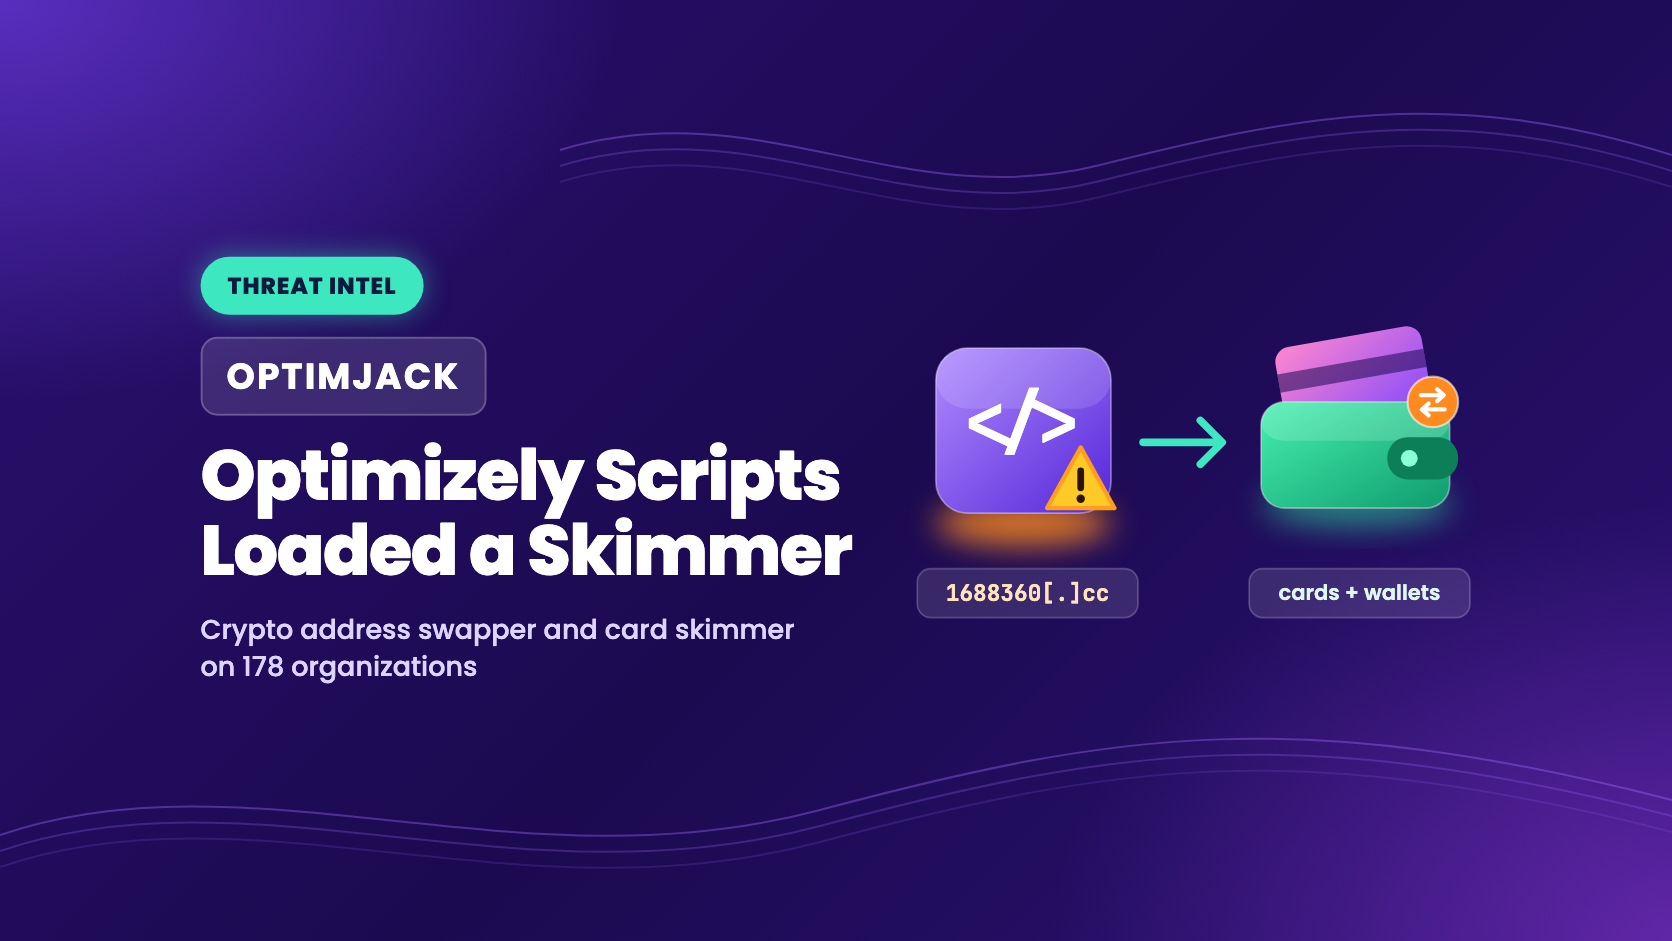
On November 16, 2026, an attacker injected malicious JavaScript into the Optimizely Web projects of 178 organizations, including CNN, BBC, Fox News, Zoom, Salesforce, GitLab, HSBC, KLM and IKEA. Optimizely's CDN served it, so every visitor to an affected site loaded it. The payload swaps copied crypto wallet addresses and steals card numbers from checkout forms. Helme's analysis says it also loads the Coruna and DarkSword exploit kits on iPhones and iPads.
Article Intelligence
Topics
Regulation Signal
in progressUpdated 3 个月前
SEC Crypto Asset Market Structure RulemakingRelated Coverage
 CryptoCrypto unicorns from 2021 boom see 50%-70% markdowns in secondary markets29 分钟前 · 1 min read
 CryptoDeutsche Bank Selects Crypto Finance for new Custody Solution2 小时前 · 1 min read
 CryptoCrypto-Native Financial Infrastructure Gets CFTC Nod2 小时前 · 1 min read
Sponsored
Ad
NewsLayer Premium
Unlock deeper intelligence.
Ad-free reading, exclusive research, and real-time onchain insights.
Go Premium