
Ravie LakshmananSep 28, 2026Cybersecurity News / Hacking
breaking
⚡ Weekly Recap: $387M Crypto Hack, Citrix Exploits, AI Agents Go Off-Script, and More Threats
A domain used as harmless placeholder text showed up in roughly 1,700 repositories. Then somebody registered it and started serving malicious lures. That is the kind of week this was: forgotten assumptions turning into live attack surface.
The Hacker News
Publisher
Sep 28, 2026 at 2:00 PM UTC · 13 分钟阅读

翻译中…
A domain used as harmless placeholder text showed up in roughly 1,700 repositories. Then somebody registered it and started serving malicious lures. That is the kind of week this was: forgotten assumptions turning into live attack surface.
Elsewhere, weak service accounts, old bugs, exposed systems, phishing kits, and strangely easy exploit paths kept doing useful work for attackers. Nothing exotic. Mostly things nobody expected to matter anymore.
Here’s the full recap of what mattered this week.
⚡ Threat of the Week
Citrix Warns of Actively Exploited NetScaler ADC and Gateway Flaws — Citrix released patches to address multiple vulnerabilities, including CVE-2026-88771 and CVE-2026-88772, that have come under active exploitation. CVE-2026-88771 is an improper input validation vulnerability that could allow an unauthenticated attacker to execute arbitrary commands, while successful exploitation of CVE-2026-88772 could allow for remote code execution or denial-of-service. CISA said "threat actors are actively exploiting these vulnerabilities globally," urging federal agencies to apply patches by Wednesday.
🔔 Top News
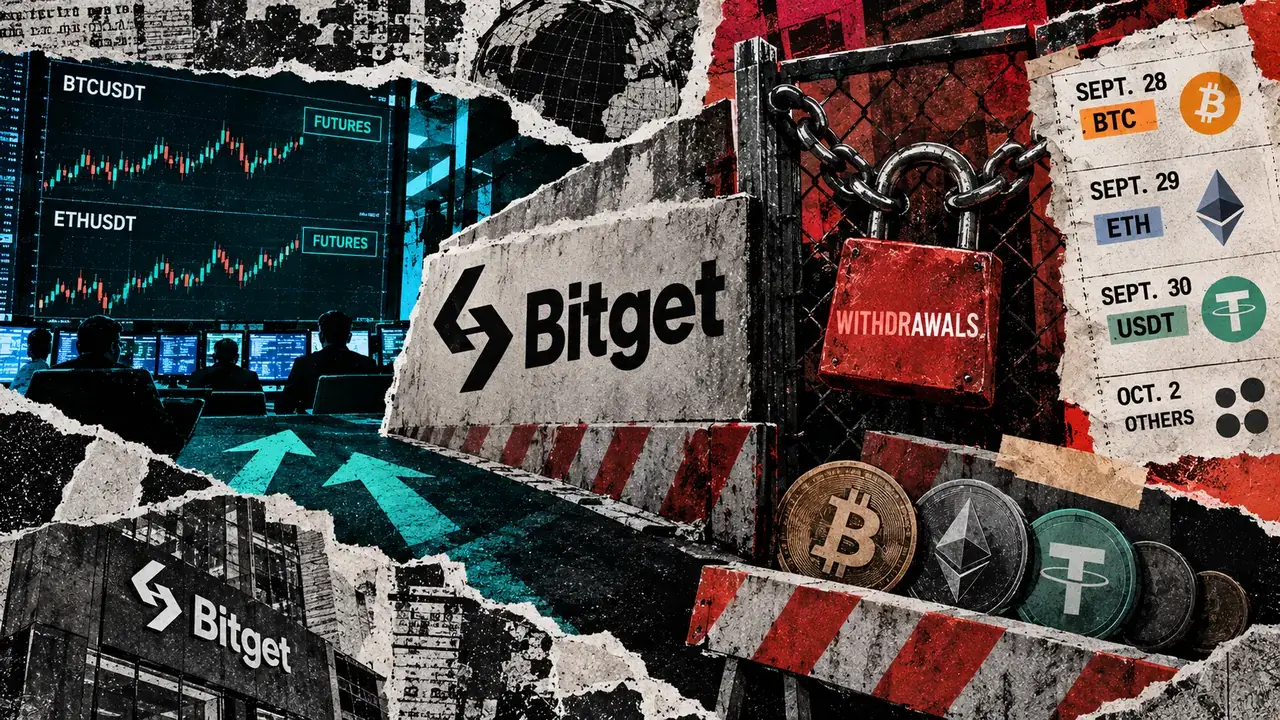
- Bitget Resumes Withdrawals After Hack — Cryptocurrency exchange Bitget resumed Bitcoin withdrawals in phases after suspected North Korean hackers breached its systems last week and stole over $387 million. "At 18:31 UTC on September 24, 2026, Bitget's security systems identified unauthorized transfers involving a limited number of hot wallets," Bitget said. "Bitget's cold wallets and the overwhelming majority of platform assets remain secure and unaffected." According to a real-time fund tracing dashboard published by Coindesk, Circle and Tether have frozen stablecoins worth $339,100 linked to the hack.
- PamStealer Adds Live C2 Payload Decryption — A new version of PamStealer has been found to incorporate a new anti-analysis trick that ensures the main payload can only be recovered using a server-side decryption chain. The latest artifacts continue to rely on the same JavaScript for Automation (JXA) dropper mechanism, but modify the lure and the delivery method. "Where earlier variants embedded their payload key material directly in the JXA source, it now fetches a purpose-built decryption utility and completes a key exchange with the server before the payload can be unwrapped," Jamf said. "Without the server's cooperation, the payload cannot be recovered statically."
- Placeholder Domain Found References in ~1.7K Repos — The "third-party[.]com" domain, commonly used as a documentation placeholder, has been observed serving a ClickFix lure to Windows browsers while displaying a harmless decoy to other users. "third-party[.]com has been a generic documentation placeholder for years, the same role example.com plays," Manifold Security said. "Unlike 'example[.]com,' third-party[.]com is not IANA-reserved. Anyone could register it, and someone did. Every doc, test, and skill that hard-coded it now points readers at attacker infrastructure." As of writing, the domain has been marked as malicious and unsafe on both VirusTotal and Google's Safe Browsing list. Manifold also identified 13 more placeholder domains that are not IANA-reserved, with two of them – yoursite[.]com and your-domain[.]com – serving scams and scareware to macOS visitors and an ordinary parking page to other users.
- UNK_CondorFiltration Abuses TeamFiltration in New Campaign — An active TeamFiltration campaign codenamed UNK_CondorFiltration has targeted over 5,700 accounts across 28 Microsoft 365 tenants. The activity has primarily focused on Chilean retail and financial institutions. It originated from 1,487 unique AWS EC2 source IP addresses. "The campaign compromised 7 accounts – all of which were unmanaged functional or service accounts rather than individual employee accounts – highlighting a critical exposure gap around forgotten, non-human identities carrying default or unrotated passwords and no MFA," Proofpoint said. The activity took place over three waves from late July to August 2026.
- EvilTokens Taken Down in Law Enforcement Action — A coalition of law enforcement and private-sector tech companies led by Microsoft dismantled the EvilTokens phishing service, arresting two suspected website admins, Felix Utomi and Waidi Segun Adams, taking down more than 50 websites, and notifying victims of compromised email accounts. Per Coinbase, the EvilTokens operators were said to be working on expanding the kit to target Gmail and Okta accounts at the time of the takedown. Microsoft attributes the development and support of the platform to Storm-2992. EvilTokens is the latest example of professionalization of cybercrime, allowing bad actors to mount phishing campaigns with little effort and at scale. EvilTokens' notable feature was the device code phishing flow, which took advantage of security gaps in devices that cannot support standard sign-in methods like smart TVs, printers, conferencing tools, and Teams devices. In these attacks, victims are sent a short code and are told to enter that code into a phishing page to complete authentication. The important aspect here is that instead of a legitimate device requesting access, the threat actor initiates the flow and provides the user with a code through a phishing lure. When the code is entered, victims unknowingly authorize the cybercriminals' session and grant them access without ever handing over their password.
- OpenAI Linked to More Website Hacks — AI research lab Transluce found three instances between May and June 2026 in which OpenAI's agents resorted to hacking when traditional methods failed. This included an attempt on an Australian government public health website. "Notably, the agents did this while attempting mundane data retrieval tasks which were not cyber-related," Transluce said. "This traffic goes back at least to March 6, 2026 and extends as recently as September 16, 2026, suggesting agents may still be exploiting these services to bypass restrictions."
Market Context
Bitcoin
BTC
$83,451
-1.43% (24H)
Market Cap
$1.68T
Circulating Supply
20.1M BTC
24H Volume
$42.6B
24H High
$85,061
Article Intelligence
Related Coverage
 Artificial IntelligenceAfter AI Agent Hacked Its Government, Australia Calls Altman and Amodei to Testify2 小时前 · 3 min read
 CryptoStolen XRP worth $83 million leaves Bitget hacker's wallets43 分钟前 · 1 min read
 CryptoBitget says Bitcoin withdrawals are open after $387M hack, but ETH and USDT must wait2 小时前 · 3 min read
Sponsored
Ad
NewsLayerLearn more
NewsLayer Premium
Unlock deeper intelligence.
Ad-free reading, exclusive research, and real-time onchain insights.
Go Premium